

HIPAA Compliance in 7 Steps: Your Ultimate Guide
Embarking on the journey to HIPAA compliance involves navigating through a structured framework of 7 essential steps. In this guide, we unravel the intricacies of ensuring the confidentiality, integrity, and availability of protected health information (PHI).
In the ever-evolving landscape of healthcare, safeguarding patient information is of utmost importance. HIPAA compliance stands as a critical framework to ensure the confidentiality, integrity, and availability of protected health information (PHI). This article will guide you through the intricacies of HIPAA compliance and provide a step-by-step approach to achieving it.
The 5 HIPAA Rules
Security Rule: The Security Rule mandates the implementation of safeguards to protect electronic PHI (ePHI). This includes administrative, physical, and technical safeguards to secure health information.
Privacy Rule: HIPAA's Privacy Rule sets the standards for protecting patients' medical records and other personal health information. It defines the rights of individuals regarding their health information and restricts the use and disclosure of PHI.
Breach Notification Rule: In the event of a security breach compromising PHI, covered entities must adhere to the Breach Notification Rule. This rule outlines the procedures for notifying affected individuals, the Secretary of Health and Human Services (HHS), and, in some cases, the media.
Enforcement Rule: The Enforcement Rule establishes the procedures for investigations and the imposition of penalties for HIPAA violations. Non-compliance can result in significant fines, making it crucial for organizations to adhere to the rules.
Omnibus Rule: The Omnibus Rule modified several aspects of HIPAA, including the expansion of liability to business associates. It reinforced the importance of compliance throughout the healthcare ecosystem.
7 Steps to Achieving HIPAA Compliance:
Embarking on the journey to HIPAA compliance involves navigating through a structured framework of 7 essential steps. In this guide, we unravel the intricacies of ensuring the confidentiality, integrity, and availability of protected health information (PHI). From conducting a comprehensive security risk assessment to implementing safeguards and designating a HIPAA compliance officer, each step is meticulously crafted to guide organizations towards a robust and secure compliance posture. Join us as we demystify the process, empowering you to safeguard patient data and adhere to the stringent HIPAA regulations with confidence.
Step 1: Conduct a Security Risk Assessment
Begin your journey to HIPAA compliance by identifying and assessing potential security risks. Evaluate vulnerabilities, implement measures to mitigate risks, and create a comprehensive risk management plan.
Step 2: Implement Safeguards
Address the Security Rule requirements by implementing administrative, physical, and technical safeguards. This may involve encryption, access controls, and regular security updates to protect ePHI.
Step 3: Designate a HIPAA Compliance Officer
Assigning a HIPAA Compliance Officer ensures accountability. This individual will oversee compliance efforts, coordinate training, and serve as a point of contact for any compliance-related concerns.
Step 4: Complete HIPAA Training for All Staff
Educate all staff members who interact with PHI on the importance of HIPAA compliance. Training programs should cover privacy policies, security measures, and the proper handling of sensitive information.
Step 5: Collect Business Associate Agreements (BAAs)
If your organization works with third-party entities that handle PHI, ensure that you have Business Associate Agreements in place. These agreements outline the responsibilities of business associates regarding HIPAA compliance.
Step 6: Establish a Breach Notification Process
Develop a clear and concise process for handling security breaches. This includes promptly identifying and reporting breaches, notifying affected parties, and taking corrective actions to prevent future incidents.
Step 7: Document Evidence of Compliance
Maintain thorough documentation of your compliance efforts. This includes policies, procedures, training records, risk assessments, and any other relevant documentation that demonstrates your commitment to HIPAA compliance.
Stress-free HIPAA Compliance with Johanson Group
Achieving HIPAA compliance is a multifaceted process that demands diligence and commitment. By following these seven steps, your organization can build a robust framework to protect patient information. For personalized assistance and comprehensive HIPAA compliance services, reach out to Johanson Group LLP. Safeguarding patient data is not just a legal requirement; it's a commitment to ethical healthcare practices.

HIPAA vs. HITRUST: What You Need to Know
HIPAA vs. HITRUST: What You Need to Know
When it comes to safeguarding personal digital information, data privacy is crucial, especially in the context of digital health records. Healthcare organizations have a responsibility to protect sensitive data using strong frameworks like HIPAA and HITRUST.
By following specific conditions outlined in HIPAA, healthcare organizations ensure that individuals have control over their personal health information.
Explore the features, requirements, and benefits of HIPAA and HITRUST compliance. Discover how these frameworks work together to protect patient data.
The Health Insurance Portability and Accountability Act of 1996 (HIPAA), a U.S. law, sets standards for healthcare organizations to ensure the security, privacy, and proper handling of protected health information (PHI). Covered entities and business associates must prioritize HIPAA compliance to avoid penalties, including significant fines and harming their reputations.
HIPAA consists of three main rules that outline specific requirements for covered entities and their business associates:
1. Privacy Rule:
The Privacy Rule establishes national standards for how healthcare organizations can use and share patients' protected health information (PHI). It ensures that individuals have control over their health information by outlining the conditions for accessing, sharing, and disclosing PHI.
2. Security Rule:
The Security Rule establishes requirements for safeguarding patients' electronic PHI (ePHI). It mandates that covered entities implement appropriate administrative, physical, and technical safeguards to protect ePHI from unauthorized access, use, or disclosure.
These safeguards include access controls, encryption, audit trails, and employee training.
3. Breach Notification Rule:
The Breach Notification Rule requires covered entities to notify affected individuals, the U.S. Department of Health and Human Services (HHS), and, in some cases, the media when a breach involving unsecured PHI occurs.
This rule ensures that individuals are quickly notified of unauthorized access or disclosure of their protected health information (PHI). It enables them to take necessary steps to protect their privacy.
HIPAA is Not The Only Compliance Framework
While HIPAA serves as a comprehensive framework for covered entities and business associates, it's important to note that it does not provide a specific roadmap or checklist for achieving compliance.
Organizations under the purview of HIPAA must conduct annual self-audits to evaluate their adherence to the regulations. It is their responsibility to establish and enforce appropriate policies, procedures, and safeguards to safeguard protected health information (PHI) and ensure compliance with HIPAA requirements.
Oftentimes, healthcare organizations face significant challenges in meeting the stringent demands of HIPAA, as well as other industry-specific and international security regulations. The implementation and maintenance of HIPAA compliance can be complex and incur substantial costs.
This is exactly where the Health Information Trust Alliance (HITRUST) comes into play.
READ MORE: An Overview of HIPAA Attestation
HITRUST offers a solution to simplify compliance efforts by harmonizing various security standards, frameworks, and regulations into a unified framework called the HITRUST CSF (Common Security Framework).
By adopting the HITRUST CSF and following the corresponding HITRUST Assurance Program, organizations can demonstrate their commitment to protecting patients' sensitive health information and upholding the integrity of the healthcare system.
HITRUST is a valuable resource for healthcare organizations, providing a comprehensive and streamlined approach to regulatory compliance and risk management.
The Role and Benefits of HITRUST Compliance for Health Organizations
Health organizations need HITRUST to navigate the complex landscape of data security and privacy regulations effectively.
The HITRUST CSF offers several benefits:
1. Simplified Compliance:
By following the HITRUST CSF, organizations can ensure compliance with various regulations, including HIPAA, GDPR, ISO, NIST, PCI-DSS, and more. It consolidates these standards into a unified framework, eliminating the need for separate assessments and audits.
2. Streamlined Risk Management:
The HITRUST CSF not only focuses on compliance but also facilitates effective risk management. It provides organizations with a structured approach to identify, assess, and mitigate risks associated with data privacy and security.
3. Reliable Certification:
HITRUST offers a certification program called the HITRUST Assurance Program, which enables organizations to obtain a recognized certification. This certification demonstrates their commitment to data security and compliance, enhancing trust among patients, partners, and stakeholders.
4. Enhanced Security:
The HITRUST CSF incorporates a comprehensive set of security controls, enabling organizations to strengthen their security posture. By adopting HITRUST's guidelines, organizations can proactively protect sensitive data and mitigate potential risks.
5. Competitive Advantage:
Achieving HITRUST certification sets organizations apart in the healthcare industry. It showcases their commitment to maintaining the highest standards of data security and privacy, which can give them a competitive edge when seeking partnerships and contracts.
By adopting HITRUST's guidelines and pursuing HITRUST certification, health organizations can ensure compliance, enhance security practices, and gain a competitive advantage.
Clarifying the Misconception: HITRUST vs. HIPAA Compliance—A Synergistic Approach
It's time to debunk the misconception that HITRUST and HIPAA are at odds. In reality, HITRUST doesn't replace HIPAA; it works hand in hand with it.
HIPAA sets the foundation for protecting sensitive health information, while HITRUST takes it a step further. By integrating HIPAA requirements with other security frameworks, HITRUST offers a more comprehensive and stringent approach to data security.
HIPAA focuses primarily on safeguarding protected health information (PHI) and establishes national standards for its use and disclosure. On the other hand, HITRUST expands on HIPAA by incorporating a broader range of security controls and requirements.
It harmonizes multiple standards, such as PCI-DSS, ISO, NIST, and GDPR, into a unified framework, creating a holistic strategy for data security and regulatory compliance.
By adopting HITRUST, organizations demonstrate their commitment to HIPAA compliance (using a HIPAA compliance audit) while bolstering their overall security posture.
HITRUST provides a robust framework that addresses a wider spectrum of security considerations, empowering organizations to establish stronger safeguards and effectively mitigate risks.
Let's dispel the misconception: HITRUST and HIPAA are not competing frameworks; they work together as complementary components of a comprehensive data security strategy.
Healthcare organizations need to understand the differences between these frameworks. This will help them improve their security practices and meet industry standards.
So, is HITRUST HIPAA-compliant?
Yes!
HITRUST incorporates HIPAA requirements into its framework, ensuring that organizations achieving HITRUST certification meet HIPAA compliance.
However, it's important to note that HIPAA compliance doesn't automatically mean HITRUST compliance. HITRUST imposes additional security controls and standards beyond what HIPAA mandates.
Real-World Examples of Compliance Requirements
HIPAA and HITRUST are two standards organizations in the healthcare industry may need to comply with. HIPAA stands for the Health Insurance Portability and Accountability Act, which sets the rules for protecting patients' sensitive health information. HITRUST, on the other hand, is a certification framework that combines various security and privacy standards, including HIPAA, to provide a comprehensive approach to managing risk in healthcare.
Some examples of organizations that may need to comply with HIPAA, HITRUST, or both, include:
1. Organizations That Need HIPAA Compliance:
Healthcare Providers:
Hospitals, clinics, nursing homes, doctors' offices, and other healthcare providers that handle patient health information are required to comply with HIPAA.
For example, a large hospital network with multiple locations must ensure HIPAA compliance to protect patient data and maintain regulatory adherence.
Health Insurance Companies:
Insurance companies that handle and process health insurance claims and PHI are also subject to HIPAA requirements.
These organizations must implement appropriate security measures to safeguard sensitive data, such as a health insurance provider managing electronic claims and medical records.
2. Organizations that Need HITRUST Certification:
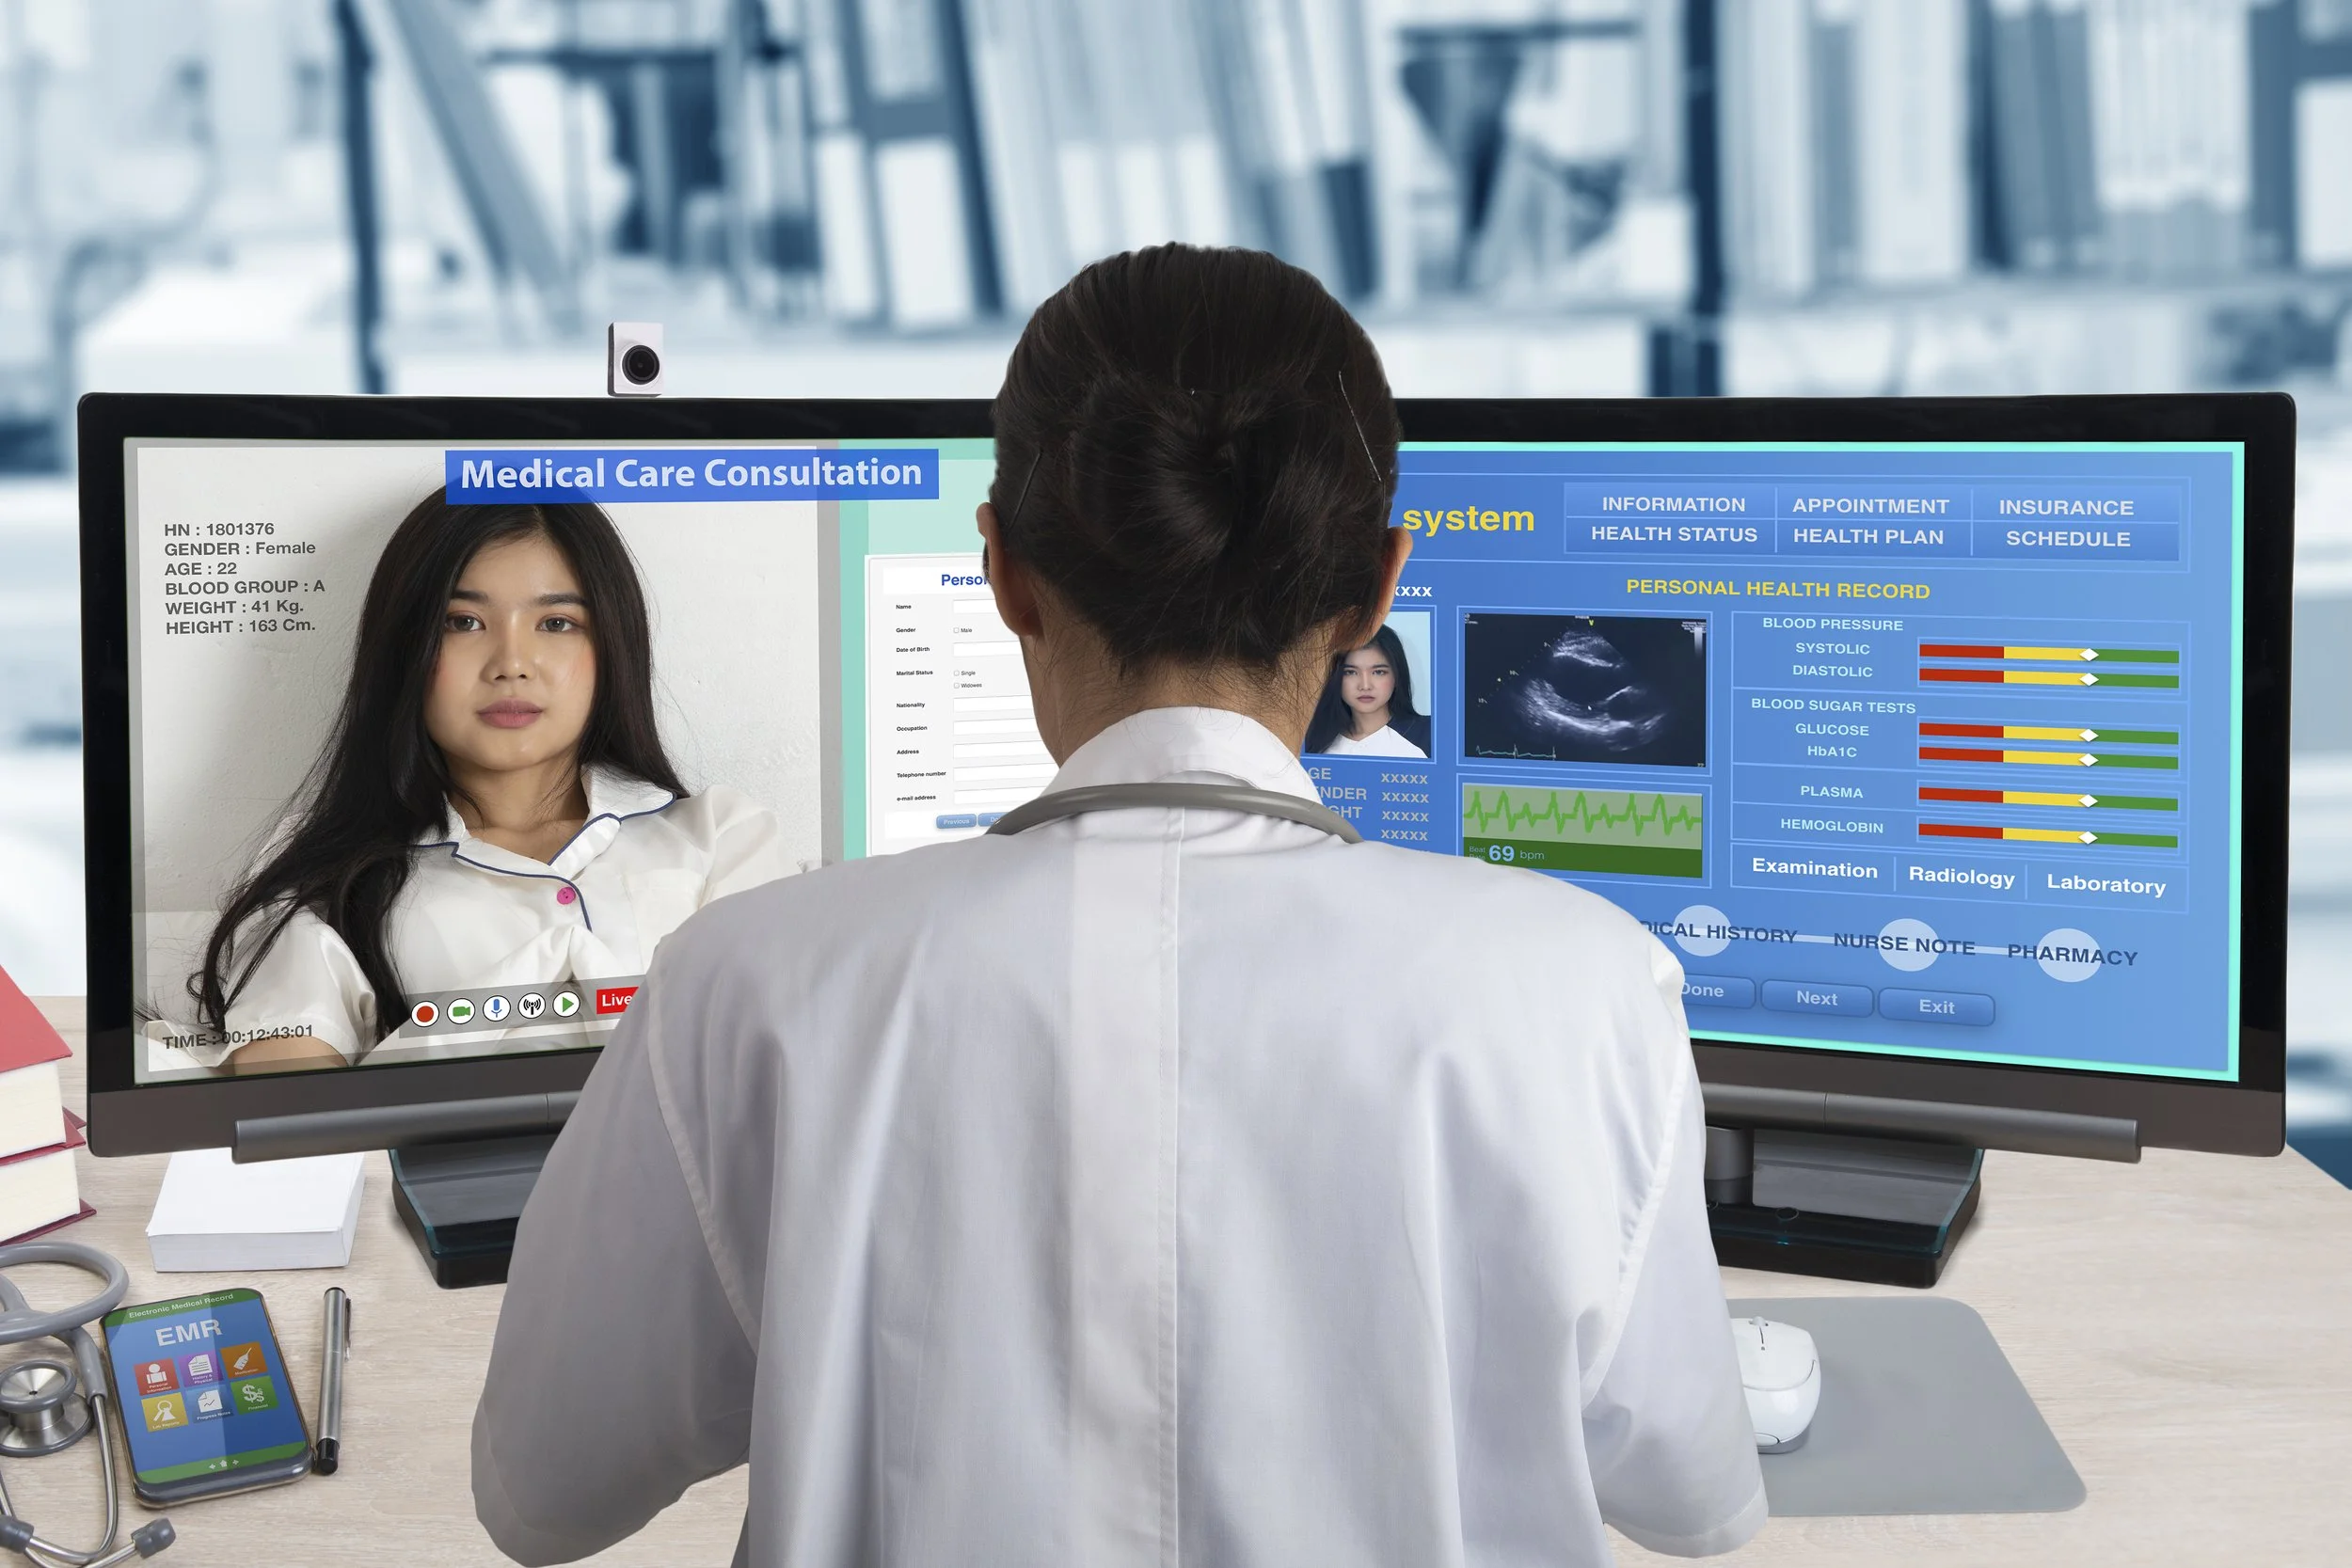
Health IT Vendors:
Organizations providing health IT solutions, including electronic health records (EHR) systems, telehealth platforms, and healthcare software applications, can benefit from HITRUST certification.
HITRUST provides a comprehensive security framework that demonstrates its commitment to data protection and establishes trust with healthcare organizations. For instance, a company offering cloud-based EHR solutions may pursue HITRUST certification to assure healthcare providers of their robust security measures.
Third-Party Service Providers:
Entities that handle, store, or process patient data for healthcare organizations, such as medical billing companies, data hosting providers, and medical transcription services, often seek HITRUST certification.
By obtaining HITRUST certification, these organizations demonstrate their commitment to maintaining the highest standards of data security and regulatory compliance.
3. Organizations needing HIPAA Compliance and HITRUST Certification:
Healthcare Clearinghouses:
Clearinghouses are crucial in processing and forwarding healthcare claims between providers, health plans, and other entities. As intermediaries in the healthcare data exchange, they must comply with HIPAA.
Additionally, HITRUST certification may be sought to enhance their security controls further and demonstrate comprehensive data protection capabilities.
Integrated Health Systems:
Large healthcare organizations that encompass multiple entities, such as hospitals, clinics, and health insurance divisions, often need to comply with HIPAA across their entire network.
Achieving HITRUST certification can provide them with a standardized and scalable security framework that aligns with their complex operations, ensuring consistent data protection practices and regulatory compliance.
HIPAA and HITRUST Are Partners in Health Compliance
Regarding data security in healthcare, organizations must carefully consider their compliance requirements.
HIPAA compliance is mandatory for entities handling PHI, while HITRUST certification provides an additional layer of comprehensive security controls.
By assessing specific security needs, scalability, and potential impact on partnerships and business opportunities, organizations can make informed decisions about pursuing HIPAA compliance audits or HITRUST certification— or both.
Ultimately, the goal is to maintain compliance, uphold patient trust, and establish a robust data security framework that aligns with the organization's objectives and future growth plans.
Partner with Johanson Group, Risk Advisory Specialists, to Safeguard Your Patient and Staff Data
At Johanson Group, we understand the importance of protecting patient and staff data in healthcare organizations.
With our expertise in risk advisory and privacy requirements, we specialize in helping healthcare organizations manage, maintain, and comply with stringent data privacy regulations.
Take Control of Your Data Security Today!
Our dedicated team of experts will work closely with you to assess your unique risk landscape, develop robust data security strategies, and implement industry-leading privacy practices.
SOC 2 and HIPAA Compliance: Similarities and Differences
SOC 2 and HIPAA Compliance: Similarities and Differences
Data security and privacy are top concerns for businesses and consumers alike. With the rise of cyber attacks and data breaches, companies are under increasing pressure to ensure the safety and protection of their customers’ sensitive information. Two common compliance frameworks that address these concerns are SOC 2 and HIPAA. While both focus on data security and privacy, they have different requirements and target different industries. In this article, we’ll explore the similarities and differences between SOC 2 compliance and HIPAA compliance.
What is SOC 2 Compliance?
SOC 2 (Service Organization Control 2) is a compliance framework developed by the American Institute of Certified Public Accountants (AICPA). It is designed to ensure that service organizations have the necessary controls in place to protect the security, availability, processing integrity, confidentiality, and privacy of customer data.
SOC 2 compliance is often required by companies that provide services to other businesses, such as SaaS (Software as a Service) companies, data centers, and IT service providers. It is also becoming increasingly important for companies that handle sensitive customer data, such as healthcare organizations and financial institutions.
Requirements for SOC 2 Compliance
To achieve SOC 2 compliance, companies must undergo a rigorous audit by a third-party auditor. The audit evaluates the company’s controls and processes related to security, availability, processing integrity, confidentiality, and privacy.
The five trust service categories that are evaluated in a SOC 2 audit are:
- Security: The protection of the system against unauthorized access, use, or modification.
- Availability: The system is available for operation and use as committed or agreed.
- Processing Integrity: System processing is complete, accurate, timely, and authorized.
- Confidentiality: Information designated as confidential is protected as committed or agreed.
- Privacy: Personal information is collected, used, retained, disclosed, and disposed of in conformity with the commitments in the entity’s privacy notice and with criteria set forth in generally accepted privacy principles issued by the AICPA and CICA.
What is HIPAA Compliance?
Overview of HIPAA
HIPAA (Health Insurance Portability and Accountability Act) is a federal law that sets standards for the protection of sensitive patient information. It applies to healthcare providers, health plans, and healthcare clearinghouses, as well as any business associates that handle protected health information (PHI) on their behalf.
HIPAA compliance is essential for healthcare organizations to ensure the confidentiality, integrity, and availability of PHI. It also helps to protect against unauthorized access, use, or disclosure of PHI.
Requirements for HIPAA Compliance
To achieve HIPAA compliance, healthcare organizations must comply with the HIPAA Privacy Rule, Security Rule, and Breach Notification Rule. These rules outline the requirements for protecting PHI and responding to data breaches.
The HIPAA Privacy Rule sets standards for the use and disclosure of PHI, while the Security Rule establishes standards for the security of electronic PHI (ePHI). The Breach Notification Rule requires organizations to notify affected individuals, the Department of Health and Human Services, and in some cases, the media, in the event of a data breach.
Differences Between SOC 2 and HIPAA Compliance
While there are some similarities between SOC 2 and HIPAA compliance, there are also significant differences that organizations should be aware of.
Target Industries
One of the main differences between SOC 2 and HIPAA compliance is the target industries. SOC 2 compliance is primarily targeted towards service organizations, while HIPAA compliance is focused on healthcare organizations.
Scope of Compliance
SOC 2 compliance has a broader scope than HIPAA compliance. While HIPAA compliance focuses on the protection of PHI, SOC 2 compliance covers a wider range of data, including financial data, customer data, and intellectual property.
Requirements for Compliance
The requirements for SOC 2 and HIPAA compliance also differ. SOC 2 compliance has five trust service categories that organizations must meet, while HIPAA compliance has three rules (Privacy, Security, and Breach Notification) that organizations must comply with.
Similarities Between SOC 2 and HIPAA Compliance
While SOC 2 and HIPAA compliance have different origins and target different industries, there are some similarities between the two frameworks.
Focus on Data Security and Privacy
Both SOC 2 and HIPAA compliance have a strong focus on data security and privacy. They both require organizations to have controls in place to protect sensitive information from unauthorized access, use, or disclosure.
Third-Party Audits
Both SOC 2 and HIPAA compliance require organizations to undergo third-party audits to assess their compliance. These audits are conducted by independent auditors who evaluate the organization’s controls and processes to ensure they meet the requirements of the respective framework.
Ongoing Compliance
Both SOC 2 and HIPAA compliance are ongoing processes. Organizations must continuously monitor and update their controls and processes to maintain compliance and address any changes in the regulatory landscape.
Achieving Compliance: Best Practices
Regardless of whether your organization needs to comply with SOC 2 or HIPAA, there are some best practices that can help you achieve and maintain compliance.
Conduct a Risk Assessment
Before beginning the compliance process, it’s essential to conduct a risk assessment to identify potential vulnerabilities and risks to your organization’s data. This will help you determine which controls and processes are necessary to mitigate these risks and achieve compliance.
Implement Strong Security Measures
Both SOC 2 and HIPAA compliance require organizations to have strong security measures in place to protect sensitive data. This includes implementing firewalls, encryption, access controls, and regular security updates.
Train Employees on Compliance
Employees play a crucial role in maintaining compliance. It’s essential to train employees on the requirements of SOC 2 or HIPAA compliance and their role in protecting sensitive data. This includes training on data security best practices, such as password protection and data handling procedures.
Regularly Monitor and Update Controls
Compliance is an ongoing process, and it’s essential to regularly monitor and update your controls and processes to maintain compliance. This includes conducting regular audits and risk assessments to identify any potential vulnerabilities and address them promptly.
SOC 2 and HIPAA compliance are two frameworks that help organizations protect sensitive data and maintain compliance. While they have some similarities, they also have significant differences that organizations should be aware of. By following best practices and regularly monitoring and updating controls, organizations can achieve and maintain compliance with these frameworks and ensure the safety and protection of their customers’ sensitive information.
Ready to enhance your compliance journey?
Contact Johanson Group today to explore our risk management reporting, assessments, and auditing expertise. Whether you're aiming for HIPAA or SOC 2 compliance, we're here to help you achieve excellence in data security and regulatory adherence.
Services


